Available for hire · Phnom Penh or remote

DevOpsEngineer

I run production on Linux, Docker, Kubernetes and Proxmox: hardened servers, CI/CD that ships on every push, backups that actually restore, and monitoring that pages before customers notice.
Location
Phnom Penh, Cambodia
Pisal Heng

Hi! I'm Pisal ✦

About the Main Character

Chapter 01 · whoami

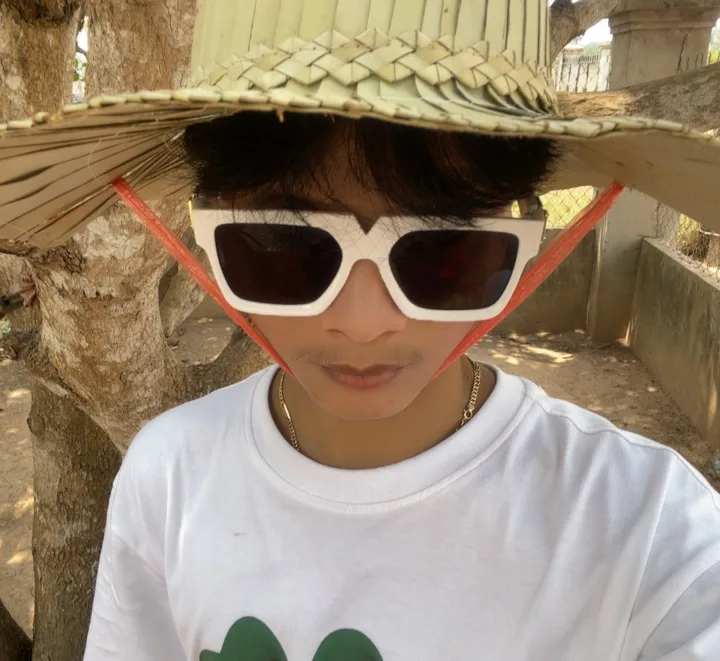
Portrait of Pisal Heng

Nice to meet you!

Pisal HENG · Phnom Penh, Cambodia
pisal@devops: ~

pisal@devops:~$ whoami

Pisal HENG — Cloud & DevOps Engineer with extensive experience in Linux administration, container orchestration, CI/CD pipelines, and infrastructure automation. Passionate about building resilient, observable systems that scale.

pisal@devops:~$ cat expertise.txt

  • Linux — Debian, Ubuntu, Red Hat, Fedora, Talos Linux
  • Containers — Docker, Kubernetes, K3s, Rancher
  • CI/CD — Jenkins, ArgoCD, Flux, Ansible
  • Security — Wazuh, Snyk, SSL/TLS, VPN, Firewalls
  • Cloud — DigitalOcean, Cloudflare, VMware, Proxmox

pisal@devops:~$ uptime

Always learning. Always building.

Core Competencies

Chapter 02 · special moves

  • 01Linux Administration

    • Debian, Ubuntu, Red Hat, Fedora, Talos Linux
    • System hardening, patching, user/group management
    • Kernel tuning, LVM, systemd, performance optimization
  • 02DevOps & CI/CD

    • Jenkins, automated testing, deployment pipelines
    • Release workflows, blue-green & canary deployments
    • GitHub Actions, GitLab CI integration
  • 03Containers & Kubernetes

    • Docker, Kubeadm, Rancher, K3s, Talos
    • Scaling, service discovery, networking
    • Container storage, ingress control, Helm charts
  • 04Infrastructure as Code

    • Ansible playbooks, roles, vault encryption; Terraform, cloud-init
    • Server provisioning, configuration management
    • Automated installation, patching, hardening
  • 05GitOps

    • Flux CD, Argo CD operators
    • Declarative infrastructure and application delivery
    • Git-based deployment workflows
  • 06Monitoring & Logging

    • Zabbix, Ntop, Komodo, Portainer
    • Prometheus, Grafana dashboards & alerts
    • ELK Stack — Elasticsearch, Logstash, Kibana
  • 07Cloud & Edge Services

    • DigitalOcean, Cloudflare DNS & CDN
    • Hostinger, Namecheap, Name.com domain management
    • Backup strategies & disaster recovery planning
  • 08Virtualization

    • VMware vSphere, vCenter administration
    • Proxmox VE clustering, Ceph storage
    • KVM, high availability, live migration, resource pools
  • 09Security

    • Wazuh SIEM, Snyk vulnerability scanning
    • SSL/TLS certificate management, Nginx hardening
    • Firewall rules, ACLs, VPN, DDoS protection
  • 10Networking & CCTV

    • NAT, VLANs, DNS, DHCP, NTP configuration
    • Fortinet, UniFi, Ruijie network equipment
    • NVR/DVR systems, remote streaming setup

Case Files

Chapter 03 · systems in production

  • File #01

    HANJAN POS

    Café point of sale, self-hosted end to end

    Problem · A café needed a POS that keeps selling when the internet drops and never loses a sale or a receipt.

    • Docker Compose stack: Next.js, Express API, PostgreSQL 17, private MinIO, Caddy, backup worker
    • Offline-first: sales queue on the device and sync with their real time when the server is back
    • Nightly pg_dump + photo backups with a tested restore script
    • Owner / cashier roles enforced by the API, not just hidden in the UI
    containers
    7
    API integration tests
    55
    nightly backups kept
    14
    • Docker Compose
    • PostgreSQL
    • MinIO
    • Caddy
    • Node.js
    • Playwright
  • File #02

    One server, many sites

    A shared TLS edge on a single VPS

    Problem · Several apps on one VPS, each wanting ports 80 and 443 and its own certificates.

    • One Caddy owns 80/443, terminates TLS and routes each domain to its stack
    • Apps join over an external Docker network, so nothing else is exposed to the internet
    • Uptime Kuma watches every service, with read-only access to the Docker socket
    public TLS edge
    1
    Compose stacks
    3
    manual cert renewals
    0
    • Caddy
    • Docker networks
    • Let's Encrypt
    • Uptime Kuma
  • File #03

    This portfolio

    Push to production in one command: git push

    Problem · Ship a static site safely with zero manual steps and a way back when a release is bad.

    • GitHub Actions: type-check, Caddyfile validation, Hadolint, image build to GHCR
    • Compose deploy gated on the container health check, with automatic rollback
    • Hardened container: non-root, read-only filesystem, all capabilities dropped, strict CSP
    pipeline stages
    4
    manual steps
    0
    health gate
    60s
    • GitHub Actions
    • GHCR
    • Docker
    • Caddy
    • Telegram alerts

The Deploy Arc

Chapter 04 · how this very site ships

01

git push

$ git commit -m "new episode"

$ git push origin main

→ GitHub Actions triggered

Here we go!

02

Test

✓ npm run build (TypeScript)

✓ caddy validate

✓ hadolint Dockerfile

No bugs shall pass.

03

Build

docker buildx build

→ multi-stage: node → caddy

→ ghcr.io/xxpisal/portfolio:<sha>

Power level rising…

04

Deploy

docker compose pull

compose up --wait → healthy

✗ unhealthy? roll back

Rolling out!

DEPLOYED!!

xxpisal.online is live

health: ok · Telegram pinged ✓

Next Episode: You?

Chapter 05 · contact

Let’s build something resilient together.

Infrastructure, CI/CD, Kubernetes, hardening, or a server that keeps falling over at 3 a.m. — I’m happy to help.

xxpisal@gmail.com

📍 Phnom Penh, Cambodia

TO BE CONTINUED ⟶

つづく

© 2026 Pisal HENG

React · Three.js · PixiJS · GSAP · Motion · Howler · Lenis — served by Caddy in Docker